Secrets vault for AI coding agents
1Password for your
AI coding agents.
Claude Code, Codex and Cursor use your API keys without ever seeing them. The agent asks, you approve the exact command, and the key exists only while it runs.
Free · local vault included · macOS (Apple silicon) · Linux and Windows via npx$ cat .env STRIPE_KEY=tramya://vault/stripe/secret $ tramya run -- stripe products list Approval required: open Tramya and confirm the run… HTTP 200 · 3 products Authorization: Bearer [tramya://redacted]
Approval request
- Agent
- Claude Code
- Command
- stripe products list
- Secret
- stripe/secret
- 1 · Reference
- 2 · Approval
- 3 · Masked output
The problem
Your agents already hold your keys.
To do their job, coding agents get access to your services. That access ends up in plain sight, in places they read all the time.
In the .env
A plain key in a file the agent re-reads every session.
In the context
Anything the agent reads can come back out in a reply, a log or a command.
Through prompt injection
A booby-trapped README or web page is enough to make it send the key elsewhere.
How it happensHow it works
The agent asks. You approve. The key stays invisible.
The agent references, it does not see
In the
.env, a reference replaces the value:tramya://vault/stripe/secret.You see the exact command
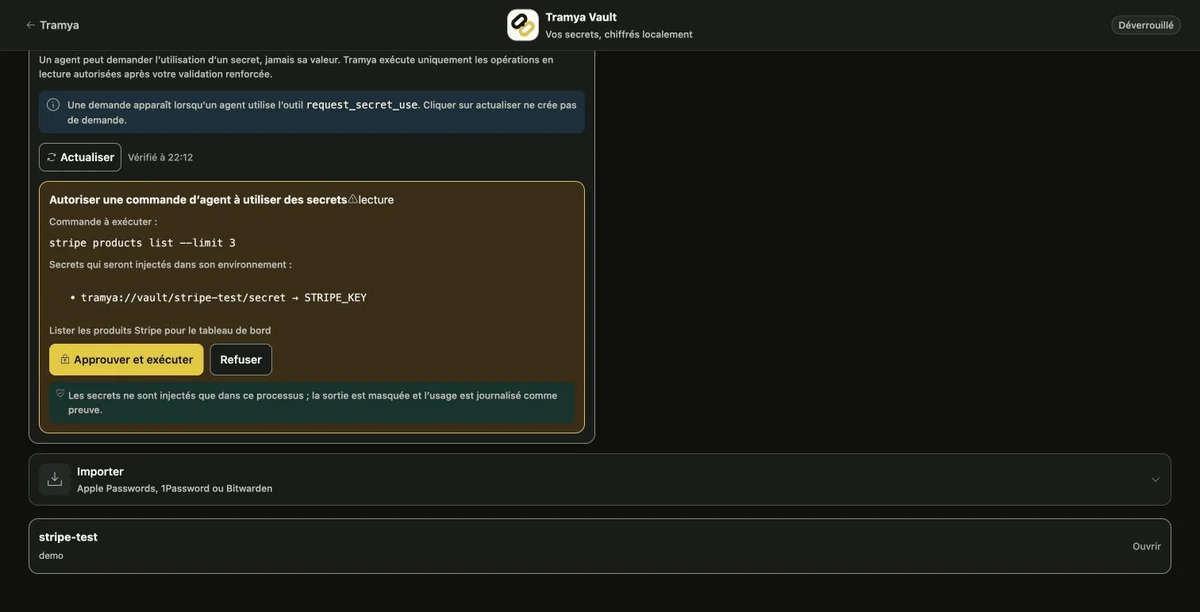
Tramya shows the command and the secrets it needs. You confirm with a second factor (TOTP code or passkey).
Injected, masked, delivered once
The value exists only inside that process. Its output is masked before it reaches the agent.
# .env
STRIPE_KEY=tramya://vault/stripe/secret

# in the agent’s terminal
tramya run -- stripe products list
Or over MCP: the agent calls request_capability itself, and you approve in Tramya.
The real screen
This is what you see, for real.
A capture of the vault interface with demo data: an agent’s request, the exact command, the second factor.
No vague promises
What Tramya guarantees. What it does not do.
What Tramya guarantees
- Local encrypted vault: AES-256-GCM, master passphrase derived with scrypt.
- No use without your approval and a second factor.
- Masked output. The value shows up neither in logs nor in clear on disk.
- The full flow is tested end to end on a clean profile.
What Tramya does not do
- It is not a sandbox: an approved command that sends its environment elsewhere sends the key too. Read the command.
- No independent security audit yet.
- Tested on macOS (Apple silicon). Linux and Windows go through the npx installer: vault not tested end to end.
- Not notarized by Apple: on first launch, right-click then Open.
- A free account is required to pair the app. The core is closed; the
tramya://format is open (MIT).
Also
Your project memory, shared across agents.
The same tool recovers decisions and context from your Claude Code, Codex or Cursor sessions and hands them to the next agent.
Frequently asked questions
How can an agent use an API key without ever seeing it?
You store the key once in the encrypted vault and reference it as tramya://vault/item/field in your .env. At run time, Tramya asks you to approve the use locally, injects the real value into the subprocess, and masks it in the output. The agent gets a working process, never the key.
Does Tramya replace Claude Code or Codex?
No. Tramya is a memory layer on top of your agents. You keep using Claude Code, Codex, Cursor or ChatGPT; Tramya links them.
Do my conversations leave my machine?
Not by default. Everything stays on your device. The encrypted Cloud vault is opt-in.
Which platforms?
The desktop app runs on macOS (Apple silicon); Linux and Windows are supported through the npx installer. Same local memory shared with the browser extension.
Can I try without a credit card?
Yes. Create a free account, install the companion, connect an agent.